JoeCyberTech
12 years protecting the digital frontier. Red Team. Blue Team. Ethical Hacker. Cybercrime Investigator. Full-Stack Developer. Based in Tokyo, Japan — operating globally.
Book a Consult View Credentials
Need a Red Team, an Investigator, or a Security Engineer?
Full-Spectrum Security From a Single, Trusted Operator
12+
Years protecting the digital frontier
Offensive Security
Nation-state APT emulation, physical & digital penetration, social engineering and C2 deployment — I find the gaps before real adversaries do.
Defensive Operations
SOC architecture, SIEM engineering (Splunk, ELK, QRadar), threat hunting, detection engineering and 24/7 monitoring strategy.
Investigation & Forensics
Darknet surveillance, cryptocurrency tracing (BTC, XMR, ETH), OSINT attribution and court-admissible evidence. Wherever they hide, I find them.
Six Disciplines. One Security Partner.
From adversary emulation to incident response, cybercrime investigation and secure development, I cover the full attack surface — so you don't need six different vendors to stay protected.
Red Team Operations
Nation-state APT emulation, physical & digital penetration, social engineering and C2 framework deployment.
Learn More
Blue Team & SOC
SOC architecture, SIEM engineering (Splunk, ELK, QRadar), threat hunting and detection engineering.
Learn More
Penetration Testing
Web, mobile, API, network, cloud, IoT and hardware — OWASP/CVSS-rated reports with exploit chains.
Learn More
Cybercrime Investigation
Digital forensics, darknet surveillance, crypto tracing (BTC, XMR, ETH) and OSINT attribution analysis.
Learn More
Secure Development
Zero-trust architecture, secure SDLC, DevSecOps pipelines and cloud hardening across AWS, Azure and GCP.
Learn More
Full-Stack Engineering
React, Node, Python, Rust, Go, PostgreSQL — custom security tooling, SIEM dashboards and breach-resistant SaaS.
Learn More
Elite Skills, Proven Under Pressure
Every credential is verifiable, every engagement is documented, and every finding ships with a clear path to remediation — one expert who has operated across offense, defense and investigation at the highest level.
0+
Years on the Frontier0
Credly-Verified Badges0+
Certifications Earned0
Security DomainsFrom Tokyo to the Front Lines Worldwide
I'm Joe — a Tokyo-based cybersecurity expert with 12+ years across offense, defense, investigation and development. I've led adversarial simulations and APT campaigns against financial institutions and government networks, and multi-jurisdictional darknet investigations for international law enforcement.
Request Consultation
Real-World Operations, Real Results
A selection of engagements across finance, government and law enforcement — adversary simulation, incident response, and cross-border cybercrime investigation.
APT Simulation — Financial Sector
Darknet Investigation — Law Enforcement
Government Network Defense
138 Credly-Verified Badges
Every badge is publicly verifiable on Credly. Here's a sample of the collection — explore the full wall for all 133.
104+ Certifications Across 7 Domains
Red Team, Blue Team, AI Security, Cloud, Development, Data & Business, and GRC — every certificate viewable and downloadable.
Discovered CVEs
Security vulnerabilities responsibly disclosed and assigned CVE or GitHub Security Advisory (GHSA) identifiers, coordinated with the affected vendors and maintainers.
More CVEs are currently in coordinated disclosure. They will be listed here as soon as the advisories are published.
coming soon// more coming — new disclosures added as they are published
DSSRF — An OWASP-Listed SSRF Defense Library
A JavaScript library I wrote and maintain: it validates and sanitizes URLs before your application makes an outbound request, so server-side request forgery never leaves the gate.
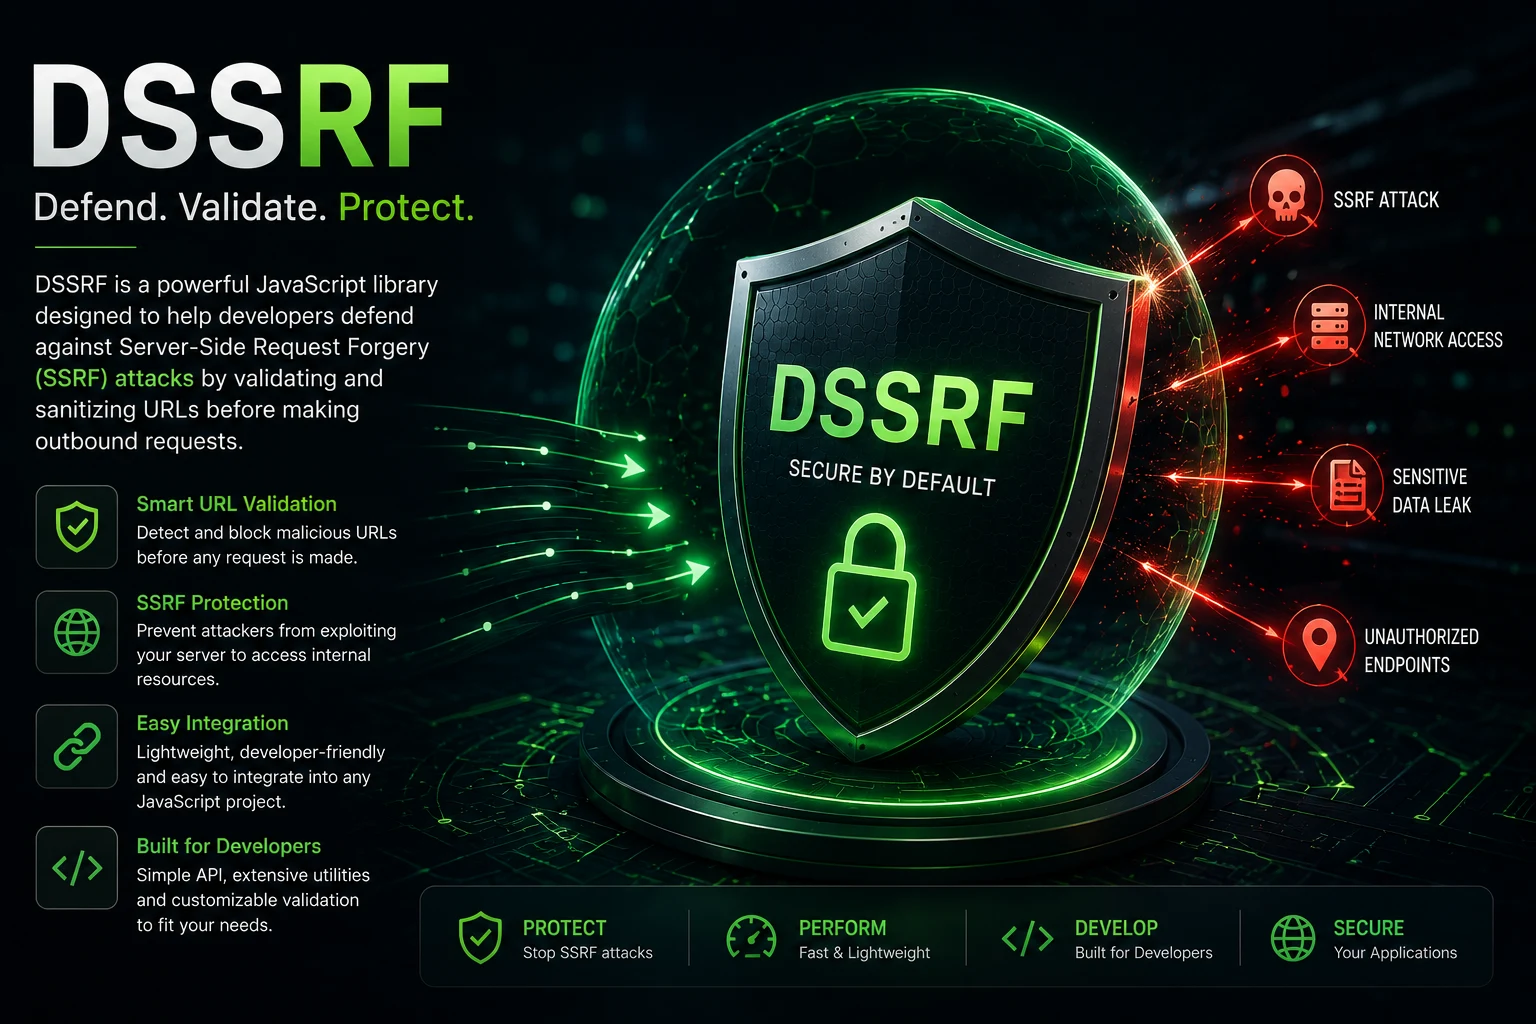
“dssrf — Defend Against SSRF attacks by providing huge of utils for validation; you integrate it with your web client before making request, you validate the url for eliminating SSRF attacks.”
— OWASP Foundation, Free for Open Source Application Security Tools (Defense Tools)
Reported to Vendors and Government Agencies
Every vulnerability I find goes through responsible, coordinated disclosure — with the affected vendor first, and with the national authorities when the impact reaches beyond a single product. Router firmware, exposed devices, malicious domains and phishing email infrastructure alike.
Multiple vulnerabilities reported against TP-Link consumer router firmware — static private keys baked into every unit, unencrypted management paths and unauthenticated administrative protocols — all disclosed through the vendor’s PSIRT process.
When a vendor is unresponsive or a product is widely deployed, I escalate through CISA’s coordinated vulnerability disclosure program. CVE-2026-58378 (network-exposed ADB) was published by CISA as VA-26-190-03.
Reported a denial-of-service flaw in CyberChef, GCHQ’s open-source “Cyber Swiss Army Knife”: the Generate Lorem Ipsum operation had no bounds check on its Length parameter and could take down a CyberChef Node backend. Coordinated with GCHQ and fixed in v11.1.1 (GHSA-hjwj-84x5-h7gr).
Criminal infrastructure surfaced during investigations — credential-harvesting kits, mule email accounts, malware distribution hosts — is referred to the FBI’s Internet Crime Complaint Center (IC3) with the supporting evidence and attribution analysis.
Cross-border issues and flaws touching critical infrastructure or public-sector systems are reported to the relevant national CERT/CSIRT and government bodies, and I stay engaged until a fix is rolled out.
Phishing domains, spoofed email infrastructure and fraud sites are mapped and reported to registrars, hosting providers, mail providers and national abuse desks so they get taken down rather than just blocked locally.
// policy — responsible disclosure only; no details published before a fix ships
CTF Achievements
Competitive hacking results from international CTF competitions — offensive skills, proven under pressure.
Finished #1 in the international contest built around UN Sustainable Development Goal 16 (Peace, Justice and Strong Institutions).
View scoreboard ↗Placed in the top 2 of the international contest built around UN Sustainable Development Goal 7 (Affordable and Clean Energy).
View scoreboard ↗Ranked top 4 out of 1888 expert engineers and hackers, building solutions for UN Sustainable Development Goal 1 (No Poverty).
View scoreboard ↗Placed 5th worldwide and 1st in Asia among more than 5000 players in a global capture-the-flag competition.
Ranked in the top 7 out of 1000 teams in Japan's premier beginner CTF — pwn, web, crypto & reversing.
View scoreboard ↗// more coming — new competitions added each season
Latest From the Blog
Field notes, threat analysis and practical guidance from the front lines of offensive and defensive security.